The Quiet Identifier: How Sites Recognise a Returning Browser
Browser fingerprinting combines visible browser traits to distinguish visits. Learn what it can reveal, how it differs from cookies, and which settings matter.
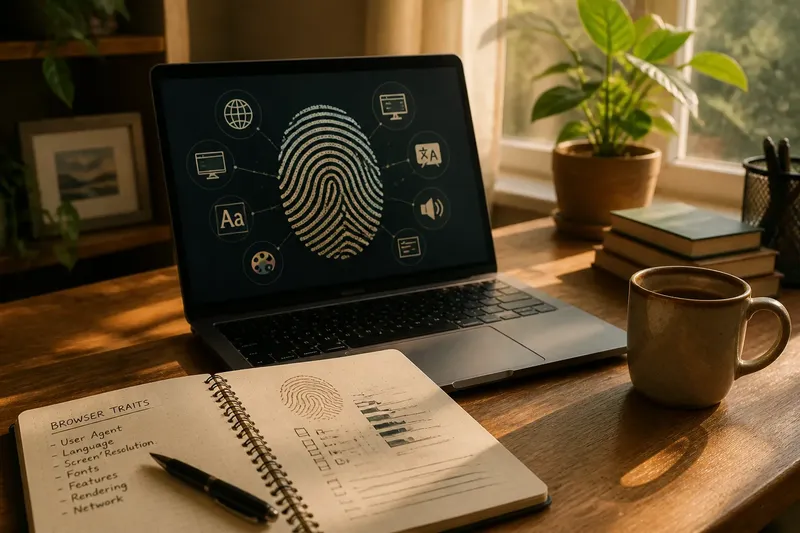
Browser fingerprinting can let a site distinguish one browser from another without storing a conventional cookie. Browser fingerprinting works by combining traits a browser exposes during an ordinary visit: its software, language preferences, screen properties and other settings. No single trait needs to identify you. The combination may be distinctive enough to recognise a returning browser, or at least to narrow down which one it might be.
That is a different claim from knowing your name. Fingerprinting is better understood as a way to link browser activity, not as a universal identity card. These field notes focus on what the technique observes, what it can and cannot establish, and which everyday choices are worth considering.
What does browser fingerprinting observe?
A browser sends information so websites can display pages and deliver compatible features. Some details appear in routine requests; others can be inferred when a page asks the browser to perform particular tasks. Taken together, these details form a profile that may help a site distinguish visits.
Commonly discussed traits include:
- Browser and operating system: Their reported names and versions help explain which web features are available.
- Language and regional preferences: These can reveal the languages the browser is set to use, and sometimes a regional format.
- Screen and display properties: Page layout may depend on the available display area, colour capabilities or pixel density.
- Installed fonts and browser features: A page may be able to infer whether certain fonts or capabilities are present.
- Rendering behaviour: Browsers can produce slightly different results when drawing text, graphics or audio through common interfaces.
- Network information: A site can receive an internet address for a connection, though that address is not itself a browser fingerprint.
These details vary in how directly they are exposed, how stable they remain, and how many other people share them. A browser’s language setting may be common. A particular mix of versions, fonts and rendering characteristics may be less common. The useful signal, if there is one, lies in the combination.
A fingerprint is not necessarily a neat, permanent string. It can be a set of observations that a service compares or combines. Different services may collect different traits and draw different conclusions. The word “fingerprint” sounds more exact than the practice always is; browsers change, observations can be noisy, and two browsers may look alike.
How is it different from cookies or signing in?
A cookie is a small piece of information a site asks the browser to keep and send back in later requests. It can carry a site-specific identifier. Browser fingerprinting instead relies on traits the browser reveals or produces; it may work without placing that kind of identifier in the browser.
Signing in is different again. An account tells a service which account is using it, subject to the service’s own systems and the details supplied. A fingerprint may help associate visits even when no account is signed in, but it does not automatically provide a person’s name, address or account credentials.
In practice, these mechanisms can be combined. A service might use an account while a person is signed in, cookies for site functions, and other browser traits for recognition or fraud prevention. Clearing cookies can remove some stored identifiers without making the browser’s remaining traits disappear. Conversely, changing browser traits does not log someone out of an account or erase records already held by a service.
That distinction matters when interpreting a privacy setting. “Block cookies” does not necessarily mean “prevent every form of recognition”. Nor does a familiar browser profile prove that a site knows who is using it. Different mechanisms answer different questions.
What can a fingerprint tell a site?
At its most modest, a fingerprint can help a service tell that two visits may come from a similar browser setup. A service could use that resemblance to keep a session coherent, reduce repeated checks, or assess whether activity looks unusual. Those are possibilities, not a promise about what any particular site does.
Recognition also has limits. A browser update can change reported traits. Installing a font, changing a display, adjusting language preferences or using a different device may alter the profile. A change may make a browser look less like its earlier self, or simply like a different member of a large crowd.
Nor does resemblance establish that the same person made both visits. A shared computer can have several users, while one person can use several browsers and devices. A public network can also put unrelated people behind a shared connection address. Fingerprinting is a clue a service may interpret, not proof of who is at the keyboard.
Imagine you use a laptop in its usual browser on Monday, then open the same site on Tuesday after a browser update. The site might observe many of the same traits and some changed ones. It could treat the visits as related, unrelated or uncertain, depending on the method and other information available; the update alone does not tell you which choice it made.
Why can ordinary browser details become distinctive?
Most traits are not remarkable on their own. A common browser, a familiar operating system and a widely used language setting may describe many people. Distinctiveness emerges when several traits are considered together, especially if some are less widely shared.
There is a practical tension here. Browsers need to disclose enough information for websites to work. A page must adapt to the browser’s capabilities; accessibility tools and language preferences serve real purposes. Removing or falsifying every observable trait is neither simple nor necessarily helpful. It can also make a browser’s combination less typical rather than more private.
Fingerprinting techniques can vary in how much information they request and how they combine it. A page that checks a small set of basic capabilities is not necessarily doing the same thing as one that collects a broader profile for recognition. From the outside, it is often difficult to tell exactly what a particular site retains or how it uses the observations.
Which questions about browser fingerprinting matter most?
Can private browsing prevent browser fingerprinting?
Private browsing generally limits what is retained locally after a private session, such as certain history and site data. It does not, by itself, hide every browser trait from a site visited in that session.
Does clearing cookies reset a browser fingerprint?
Clearing cookies removes stored site data covered by the browser’s clearing controls, but it does not necessarily change the browser’s language, display, software or other observable traits. It may interrupt cookie-based recognition while leaving other forms of comparison possible.
Can a site identify me by my browser fingerprint alone?
A fingerprint may help distinguish or link a browser profile, but it does not inherently reveal a real-world identity. A service could connect it with information it already has, such as an account or details supplied during a visit; the fingerprint alone is not a name tag.
Will changing browser settings make me harder to recognise?
Some settings affect what a browser exposes, and privacy-focused browsers may limit or standardise certain signals. Results depend on the browser and the site, while unusual combinations of changes can create their own distinctive profile.
Which privacy choices are worth the effort?
Start with the browser’s built-in privacy and tracking protections. Review what they say they block or limit, and keep the browser maintained so its controls and security fixes remain current. A browser designed to reduce cross-site tracking may also limit some fingerprinting techniques, though the details differ between products.
Use separate browser profiles when there is a clear reason to keep activities apart, such as separating personal browsing from a work account. Profiles can reduce accidental mixing of cookies, sign-ins and settings. They do not make the two profiles invisible to every observer, and using a collection of elaborate profiles can become its own hobby.
Consider whether an extension is reputable and necessary before adding it. Extensions can ask for access to pages or browsing data, and some alter the browser traits a site can observe. Installing many tools in the name of privacy may increase complexity without giving a clear account of what is shared.
It is usually not worth repeatedly changing screen settings, installing obscure fonts or spoofing individual browser details in an attempt to look anonymous. Those adjustments can break pages, create an unusual combination, or produce little practical benefit. Prefer understandable protections that work consistently over a private browser costume assembled one setting at a time.
Where a site offers a privacy or tracking control, read the description and choose according to what the service says it changes. A control may address advertising cookies, personalisation or another specific use rather than all browser recognition. The label and the scope matter more than its reassuring name.
What should you remember during an ordinary visit?
Browser fingerprinting describes recognition through a collection of observable traits, not a magic identifier that always follows one person everywhere. Cookies can store identifiers; account sign-ins can directly associate activity with an account; browser traits can help services distinguish or compare visits. They may operate together, but they are not interchangeable.
If a site seems to remember a browser after cookies are cleared, that observation does not establish fingerprinting. The site may have retained an account session, used another storage method, or applied a different recognition technique. The sensible response is to check whether you are signed in, review the browser’s site-data controls, and consult the site’s privacy information if the distinction matters to you.
For browser fingerprinting, the useful everyday question is not whether every trace can be erased. It is which traits a browser exposes, what protections its settings provide, and whether a particular site needs the information it requests. That keeps the subject in proportion: a real privacy consideration, but not a verdict on who you are.